Call: 1-916-358-6449
Is my website contact form a HIPAA violation? It can be, once the form collects protected health information (PHI). A HIPAA compliant web form encrypts that data, stores it securely, and runs under a signed agreement with every vendor involved.
For Houston clinics, this matters more each year. Patients now book visits, ask questions, and describe symptoms online. Meanwhile, many practice sites still send those messages through plain email.
I have built healthcare websites since 2004. Across that work, the contact form is usually the weakest link. This guide shows what to fix first. It also helps if you plan a website redesign, new medical practice website design, or SEO for home care agencies.
Note: This article is technical guidance, not legal advice. Please confirm your setup with your HIPAA compliance officer or healthcare attorney.
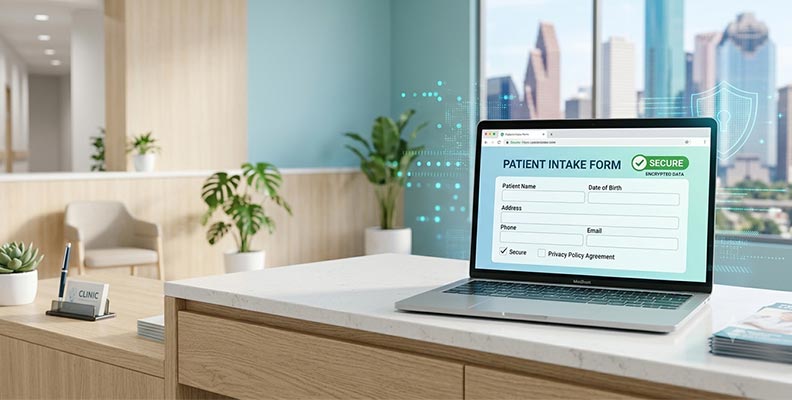
A HIPAA compliant web form protects PHI from the moment a patient types it until it is deleted. That means encrypted transmission, secure storage, limited access, and activity logs. Equally important, every vendor handling the data must sign a Business Associate Agreement (BAA).
PHI is any health detail tied to a person, such as a name plus a symptom. Electronic PHI (ePHI) is that same data in digital form. Once your form captures it, the HIPAA Privacy Rule and Security Rule both apply.
Software alone does not make a form compliant, though. Instead, compliance comes from the tool, its setup, and your office procedures working together.
A contact form becomes a risk when it collects health details without proper safeguards. Common examples include symptom boxes, insurance fields, and appointment reasons. If that data travels by plain email or sits in an unprotected database, your practice may be exposed.
Here are the patterns I see most often on Houston clinic sites:
Notably, a general inquiry with only a name and phone number carries far less risk. Trouble starts when patients volunteer medical details. So, is your website contact form HIPAA compliant? Usually not, unless someone built it for PHI.
A general contact form can safely collect basic details that reveal nothing about health. Typical examples include names, phone numbers, email addresses, and preferred contact times. Once a field asks about symptoms, medications, or insurance, the form needs full HIPAA safeguards.
Context still matters, however. For a specialty clinic, even a name may imply a condition. Therefore, I recommend a simple rule: collect the minimum, and route anything clinical through a secure channel.
Lower-risk fields for a public contact form:
Fields that need a secure, HIPAA-ready form:
A short note under the message box also helps. Ask visitors not to share medical details there.
Every HIPAA compliant web form needs several safeguards working together. These include a signed BAA, encryption in transit and at rest, role-based access, audit logging, and documented retention. Missing any single layer can leave patient data exposed, even when the form looks secure.
The HHS Office for Civil Rights (OCR) enforces these rules. Meanwhile, the HITECH Act strengthened enforcement and the Breach Notification Rule. [external link: HHS.gov summary of the HIPAA Security Rule]
Popular WordPress plugins are not HIPAA compliant out of the box. Contact Form 7 sends entries by email, while WPForms and Gravity Forms usually store them in the site database. Standard setups rarely include a BAA or PHI-grade encryption, so extra configuration or a dedicated tool is needed.
Contact Form 7 HIPAA concerns usually come down to email. Standard notifications copy the full message into inboxes, phones, and backups. Consequently, PHI ends up in places your practice cannot track.
WPForms and Gravity Forms add entry storage and file uploads. That convenience creates another copy of patient data on your web server. Unless the server, database, and backups are encrypted and covered by a BAA, that copy becomes a liability.
In my projects, a WordPress HIPAA form usually follows one of two paths:
Either way, the alert email should simply say a new submission arrived. It should never contain the patient’s message.
The right HIPAA compliant form builder signs a BAA, encrypts data everywhere, and limits staff access. It should also log activity and let you control retention. Beyond compliance, it must embed cleanly, work well on phones, and avoid slowing your pages.
Use these criteria when comparing options:
Entry-level plans often exclude the BAA. Therefore, confirm the exact plan before you build anything.
Tracking pixels can leak PHI even when the form itself is secure. Scripts from ad and analytics platforms may capture page URLs, clicks, or form events. On appointment and intake pages, that data can link a person to a health service.
HHS OCR has issued guidance on online tracking technologies for covered entities. Later, a federal court in Texas limited part of that guidance in 2024. However, the core risk remains whenever identifiable health data reaches a vendor without a BAA. [external link: HHS.gov guidance on online tracking technologies by HIPAA covered entities]
Practical steps I use on healthcare sites:
Texas adds its own privacy layer through Texas HB 300, the Texas Medical Records Privacy Act. It defines covered entities more broadly than HIPAA does. As a result, some Houston businesses outside traditional healthcare may still have duties around health information.
Generally, HB 300 adds staff training duties and stricter limits on sharing health data. It also sets expectations for giving patients electronic copies of their records. Because these rules overlap with HIPAA, your web forms should satisfy both.
Across Harris County, practices also compete hard for patients online. Clinics near the Texas Medical Center, in Sugar Land, Katy, The Woodlands, Pearland, and Bellaire all fight for the same searches. A secure, clear form builds trust before the first visit.
State rules also evolve. For that reason, confirm current requirements with a Texas healthcare attorney. [external link: Texas Attorney General overview of health information privacy]
Good medical practice website design treats forms as part of the security plan. A website redesign is often the best time to fix form risk. It lets you rebuild forms, hosting, and tracking together instead of patching each one separately.
As part of web development in Houston, TX, a typical form upgrade includes:
Home care agencies collect sensitive details from families, often about aging parents. Care needs, diagnoses, and insurance questions appear in inquiry forms daily. Pairing secure intake with SEO for home care agencies helps families find you and trust you.
AI search tools favor sites that answer questions clearly and show real expertise. Similarly, a visible privacy note and secure intake process strengthen trust signals. My AI SEO services connect that technical work with visibility in Google and AI answers.
Use this checklist to review any HIPAA compliant web form on your site. It covers vendors, encryption, access, tracking, and staff habits. If you cannot confirm an item, treat it as a gap and fix it before collecting more patient data.
HIPAA Compliant Web Forms in Houston – What Clinics Must Have Before Collecting Patient Data
Houston Roofing SEO in 2026: How Roofers Win Google Maps & AI Search
How Houston memory care facilities rank in Google Maps and AI search in 2026
Hire an SEO Expert For Roofers in Houston to Generate More Roofing Leads and Grow Your Roofing Business Faster
Get Local SEO for Auto Appraiser Services in Houston With Transparent Monthly Pricing From DBanerjee.com
SEO consultant for roofing and construction: How Houston contractors win more local leads
SEO consultant for roofer in Houston: What monthly roofing SEO really delivers
It can be. If the form collects health details, such as symptoms or insurance data, it handles PHI. Without encryption, secure storage, and a signed BAA with each vendor, that creates real compliance risk for your practice. A quick form review shows whether your current setup needs small changes or a full website redesign.
A HIPAA compliant web form encrypts data in transit and at rest. It also limits staff access, keeps audit logs, and follows written retention rules. Most importantly, every vendor handling the data must sign a Business Associate Agreement. Software alone is never enough; setup and office procedures matter too.
Not by default. Contact Form 7 sends submissions by email, so patient details land in inboxes, phones, and backups. For clinics, a better approach is a secure form from a BAA-backed vendor. Alternatively, a developer can configure encrypted storage with notification-only emails that never include PHI.
Standard Google Forms setups are not HIPAA compliant by default. A BAA through a qualifying Google Workspace plan may help. Even so, configuration still matters a great deal. For Houston clinics, a dedicated HIPAA compliant form builder is simpler and safer for patient intake and appointment requests.
A basic contact form can usually collect a name, phone number, email, and preferred callback time. Once you ask about symptoms, medications, insurance, or medical history, the form needs full HIPAA safeguards. When in doubt, collect less and move clinical details to a secure, BAA-covered channel instead.
Yes, it can. Texas HB 300 defines covered entities more broadly than HIPAA and adds staff training duties. It also limits how health information is shared. Houston practices should make sure web forms, staff habits, and vendors meet both federal and Texas rules. Confirm details with a Texas healthcare attorney.
They create real risk. Pixels can send page visits or form events to ad platforms. That data may link a person to a health service. HHS OCR has issued guidance on online tracking technologies. Remove ad pixels from booking and intake pages, and keep identifiable health data out of every analytics tool.
Many do. Families often share diagnoses, care needs, and insurance details through inquiry forms. If your agency bills health plans, HIPAA likely applies, and Texas HB 300 may reach further. Pairing secure intake with SEO for home care agencies helps families find you and trust you with sensitive details.
Not always, but it often helps. A website redesign lets you rebuild forms, hosting, and tracking together rather than patching each piece. It is also a chance to improve medical practice website design, page speed, and mobile usability. A form audit first shows whether a fix or rebuild makes more sense.
Look for a developer with real healthcare website experience. DBanerjee.com offers web development in Houston, TX, including secure form setup, tracking cleanup, and AI SEO services. Dipankar Banerjee has built websites since 2004 and works directly with each client, with no outsourcing or account managers.
A HIPAA-compliant web form is now a basic expectation for Houston clinics. Patients share private details online, and they assume you will protect them. Fortunately, most form risks are fixable with the right tools, setup, and habits.
Start by mapping your forms and checking each vendor for a BAA. Next, remove tracking from sensitive pages and clean up email alerts. If your site needs bigger changes, a website redesign or new medical practice website design may be the cleaner path.
I work directly with practices across Houston, Sugar Land, Katy, and The Woodlands. Together, we can review your forms, plan secure intake, and support visibility through SEO for home care agencies and AI SEO services.
Ready for a second set of eyes on your site? Book a free consultation and website form review with DBanerjee.com for web development in Houston, TX.